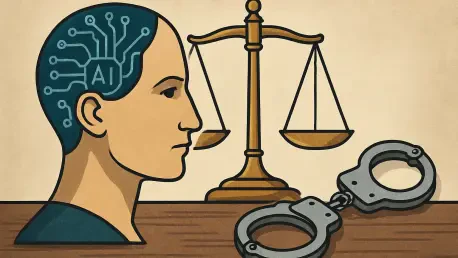
Under the proposed laws, AI companies must maintain rigorous security controls throughout the entire lifecycle of a model, from its initial development to final deployment. The Australian federal government has signaled a transformative shift toward establishing the most stringent regulatory environment for artificial intelligence seen globally. By transitioning from voluntary guidelines to a robust, legally enforceable framework, the Albanese administration aims to prioritize public safety without stifling the economic innovation that characterizes the tech landscape. This proposal introduces mandatory security standards for frontier AI companies and explores criminal liability for corporations whose models lead to substantial harm. This move signals Australia’s intent to become a global leader in AI governance, setting a precedent for how nations manage the risks of advanced technology while securing the digital economy against emerging threats in this era of rapid growth.
Legislative Frameworks and Technical Oversight
The proposed regulatory structure operates on two primary paths designed to ensure technical oversight and corporate accountability in an increasingly automated society. The first path establishes AI standards legislation, creating a dedicated regulator alongside the Australian AI Safety Institute to monitor high-risk models with technical precision. This body will enforce mandatory security controls backed by the threat of heavy financial penalties, ensuring that the development phase is not neglected in favor of rapid market entry. By establishing these technical guardrails, the government seeks to move beyond conceptual safety toward a practical reality where AI systems are audited for algorithmic bias and systemic vulnerabilities before they interact with the public. This approach reflects a growing consensus that the era of self-regulation has ended, replaced by a system where governmental oversight is as rigorous as the safety checks found in aviation.
Mandatory Standards for High-Risk Systems
Under these new standards, frontier AI companies must adhere to strict operational protocols to maintain their legal standing and avoid catastrophic failures. These include continuous risk management to identify potential threats in real-time, independent third-party evaluations to verify safety claims, and a rapid incident reporting system for any security breaches that occur post-deployment. Furthermore, transparency is a core requirement, as companies must publicly disclose their governance frameworks to allow for external scrutiny by civil society and academic researchers. These obligations ensure that security is treated as a continuous process rather than a one-time check during the initial development phase, forcing developers to account for how their models might evolve through interaction with data. By mandating such transparency, the law creates a feedback loop where the public can understand the limitations and safety measures of the tools they use.
Operational Protocols and Data Transparency
Building on these technical foundations, the legislation also addresses the specific handling of training data and the prevention of adversarial attacks. Companies are now required to maintain detailed logs of data sources and processing methods, which the regulator can audit at any time to ensure compliance with privacy and intellectual property standards. This level of oversight is designed to prevent the accidental or malicious ingestion of sensitive information that could lead to data leakage in generative models. Additionally, firms must demonstrate that they have implemented robust defense mechanisms against prompt injection and other emerging exploitation techniques. By focusing on the integrity of the data pipeline, Australia is attempting to secure the very foundation of artificial intelligence, ensuring that the outputs generated by these complex systems remain reliable and safe for deployment in critical infrastructure and public service applications.
Corporate Liability and Economic Impacts
Perhaps the most aggressive aspect of the proposal is the introduction of a criminal “failure to prevent” offense for AI developers, a concept that mirrors modern anti-bribery and corruption laws. This legal mechanism would hold companies responsible if their technology is used for harmful purposes and they cannot prove they took reasonable steps to prevent such misuse during the design phase. Prompted by high-profile data breaches and security gaps in existing systems, this move signals a departure from traditional liability models that often struggle to assign blame in decentralized tech environments. It places the burden of safety squarely on the creators, suggesting that “not knowing” how a model might be misused is no longer a valid legal defense in an age where systemic risks are foreseeable. This proactive stance forces executives to integrate ethical considerations into the very architecture of their models, ensuring safety is a priority.
The Failure to Prevent Criminal Offense
Legal experts caution that while criminal liability serves as a powerful deterrent, the “black-box” nature of large-scale models presents unique hurdles in a traditional courtroom setting. Proving foreseeability and criminal negligence requires a level of technical clarity that current judicial systems may struggle to interpret effectively without specialized assistance. Some scholars suggest a tiered approach might be more practical, where civil penalties address unreasonable conduct while criminal charges are reserved for instances of reckless disregard for human safety or national stability. This would provide regulators with a more nuanced toolkit for different levels of corporate failure, allowing for flexibility as the technology continues to advance. The debate over proof remains central to the implementation, as courts will need to determine whether a hallucination or a malicious exploitation resulted from corporate negligence or an inherent limitation of the technological paradigm.
Business Integration and Human Oversight
The broader business community is closely watching how these regulations will affect enterprise-level AI, which integrates technology into daily corporate operations rather than just research labs. Industry leaders argue that most organizations are consumers of AI rather than developers of frontier models, meaning the law must distinguish between these roles to avoid stifling general business adoption. For the legislative framework to succeed, it must support clean data and human oversight as the foundation of secure business integration across sectors like finance, healthcare, and logistics. This perspective ensures that AI remains a tool for enhancing human judgment rather than replacing it entirely, maintaining a human-in-the-loop requirement for sensitive decisions. By focusing on the user end of the spectrum, the government can protect smaller firms that utilize these tools while holding the primary developers accountable for the safety of the engine.
Future Directions for Global Governance
As the legislative process reached its final stages, stakeholders across the industry began to adapt to the reality of a significantly altered digital landscape. Many organizations prioritized internal audits of their AI portfolios, ensuring that governance frameworks aligned with the proposed safety standards to mitigate the risk of litigation. The shift toward potential criminal liability established a new precedent where technical compliance alone was considered insufficient; instead, a demonstrated culture of safety became the expected norm for corporate conduct. Analysts observed that the focus of the debate transitioned toward international harmonization, as Australia’s stance inspired similar frameworks in neighboring jurisdictions. This movement effectively created a new global standard for corporate accountability in the tech sector. Early adopters who embraced these standards found themselves at a distinct advantage, having secured a level of public trust that was previously unattainable.