A stark warning from November 2026 indicates that AI-powered hackers are now launching record-breaking crypto heists that could shatter public trust in digital banking services. As autonomous agents become increasingly sophisticated at reconnaissance and social engineering, the risk to corporate treasuries and digital asset holdings has moved from theoretical to an immediate existential threat. These automated campaigns do not merely aim for individual wallets; they target the very connectivity and trust frameworks that underpin modern financial services, including crypto banking, payroll systems, and cross-border payment processors. For businesses that have integrated digital assets into their daily operations to leverage speed and lower transaction costs, the emergence of high-speed, AI-driven exploits necessitates a complete rethink of defensive strategies. Security is no longer just about maintaining a strong perimeter but about ensuring the integrity of every transaction flow and identity verification process in an environment where adversaries can learn and adapt in real time.
The current landscape of financial technology sees a convergence of traditional fiat banking and decentralized finance, creating a concentrated attack surface that few organizations are fully prepared to defend. This integration allows for unprecedented efficiency in global commerce but also provides a playground for AI agents capable of executing multi-stage attacks across different currency rails simultaneously. When an organization utilizes a crypto banking platform for managing multi-signature treasuries or automated bill payments, an undetected breach could drain operating funds across various denominations before human intervention is even possible. The erosion of confidence resulting from these incidents threatens to reverse years of progress in digital asset adoption. Consequently, business leaders must move beyond accepting generic security marketing and instead implement rigorous, verifiable protocols that address the unique challenges posed by autonomous hacking technologies.
1. Step 1: Examine the Custody Infrastructure Layout
To safeguard organization’s capital from sophisticated autonomous attacks, the first essential action involves requesting a detailed diagram of the platform’s storage architecture. This technical overview must provide a transparent look at where private keys are held and how they are managed during the lifecycle of a transaction. A robust defense in 2026 relies on the utilization of Hardware Security Modules (HSM) or Multi-Party Computation (MPC) vaults, which distribute the signing process across multiple points to prevent a single point of failure. It is critical to confirm that the service provider cannot move funds unilaterally; the architecture should be designed so that the business retains ultimate control over its assets, even if the platform’s primary interface is compromised by an external AI agent. Understanding the physical and logical separation between the platform’s operational layer and the actual asset custody layer provides the foundation for all subsequent security measures.
The necessity of this structural examination is further highlighted by current regulatory expectations, including the FDIC’s 2026 guidance on crypto-asset safekeeping. This guidance emphasizes that financial platforms must clearly distinguish between custodial and non-custodial models to define liability and protection levels accurately. For a business, this means verifying that their digital assets are stored in segregated, insured infrastructure rather than being commingled with the platform’s own operational capital. AI-driven campaigns often look for weaknesses in how platforms bridge different services; therefore, ensuring that the custody layer remains firewalled from payment routing and card issuance is vital. By validating that the custody provider employs qualified, institutional-grade standards, a finance lead can ensure that a breach in one part of the banking stack does not lead to a catastrophic loss of the entire treasury.
2. Step 2: Confirm the Separation of Login and Authorization
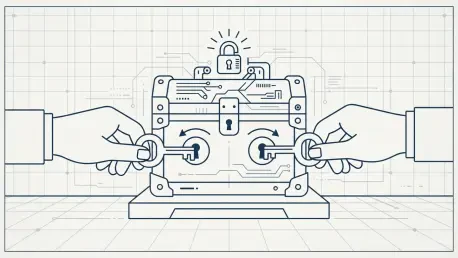
The second critical step in hardening a business against AI threats is to verify that the credentials used to access an account are entirely separate from those used to approve the movement of money. In the current cybersecurity environment, AI agents are remarkably proficient at session hijacking and credential stuffing, often bypassing traditional password protections with ease. If the same authentication factor that grants entry to a dashboard also authorizes a million-dollar wire transfer, the organization is inherently vulnerable. Security protocols must mandate that transaction signing occurs in a completely independent environment, requiring a distinct set of approvals that an AI cannot replicate simply by stealing a session token or mimicking a user’s login behavior. This architectural decoupling ensures that even if an attacker gains visual access to an account, they remain unable to execute outbound transfers.
Implementing this separation often requires the use of hardware keys and isolated signing environments that remain disconnected from the primary web interface. Since AI-generated social engineering can frequently trick employees into revealing one-time passwords or clicking malicious links, hardware-based multi-factor authentication (MFA) serves as a necessary physical barrier. These devices ensure that a transaction cannot be finalized without a physical action from an authorized user, a step that currently remains outside the reach of remote autonomous software. Furthermore, businesses should investigate whether their banking partner supports transaction-specific signing keys that are generated and stored on a device controlled by the company, not the service provider. This approach neutraluates the risk of a compromised platform-side API, as the final signature must come from a source the AI has not yet infiltrated.
3. Step 3: Perform a Permission Matrix Stress Test
Internal threats and the sophisticated reconnaissance performed by AI require organizations to conduct regular stress tests of their permission matrices. A business should set up a trial sub-user account with limited privileges and attempt to process a high-value wire transfer or a cryptocurrency withdrawal. This test reveals whether the platform’s role-based access control (RBAC) is functioning as intended or if there are latent vulnerabilities that an autonomous agent could exploit to escalate privileges. A secure platform must demonstrate the ability to block unauthorized attempts and immediately flag the activity for review. This proactive evaluation ensures that the granular permissions configured for different team members—such as accountants, executives, and treasury managers—are strictly enforced and cannot be bypassed through simple logic errors in the software.
Beyond individual permissions, the stress test must also confirm the effectiveness of dual-approval workflows. No high-value transaction should ever be executable by a single person; instead, a secure system requires at least two authorized individuals to sign off on any movement of funds that exceeds a specific, pre-configured threshold. This “two-man rule” is a cornerstone of institutional finance that is now more relevant than ever in the context of AI-driven fraud. By enforcing these thresholds, an organization creates a mandatory delay and a human-in-the-loop requirement that prevents an AI from draining an account in a matter of seconds. For decentralized autonomous organizations (DAOs) and startups, these workflows must be hard-coded into the treasury management interface, ensuring that the governance of funds remains resilient against both external hacking and internal compromise.
4. Step 4: Evaluate the Logic Behind Anomaly Detection
Protecting assets in 2026 requires more than static rules; it demands an evaluation of the logic behind the platform’s anomaly detection systems. Businesses must inquire how a system identifies and halts suspicious activity, such as a large transfer to a previously unknown address initiated during non-business hours. Modern defense mechanisms should utilize AI-driven behavioral analysis to establish a baseline of normal activity and then trigger immediate freezes when deviations occur. This is particularly important for detecting “low and slow” attacks, where an autonomous agent attempts to drain small amounts over a long period to avoid triggering basic volume alerts. Understanding the specific parameters that define “suspicious” allows finance leads to tailor their security settings to the unique operational rhythm of their global business.
Furthermore, it is essential to ensure that these protective triggers apply equally to traditional fiat wire transfers and digital asset movements. Many platforms have separate monitoring systems for different currency rails, which can create blind spots that sophisticated attackers are quick to exploit. A unified security approach monitors the entire transactional flow, regardless of whether the asset is USD, EUR, or a stablecoin. This cross-rail monitoring is vital for organizations that frequently use on-ramps and off-ramps to move capital between the traditional banking system and the blockchain. By demanding a high level of sophistication in how a banking partner flags pattern manipulation, a business can leverage the same technology being used against them—artificial intelligence—to act as a real-time guardian of their financial interests.
5. Step 5: Review the History of Security Incidents
A transparent security culture is often the best indicator of a platform’s reliability, making a review of the history of security incidents a mandatory part of any due diligence process. Businesses should ask for a record of past breaches, security audits, and sanitized post-mortem reports. A company that provides detailed information on how they handled previous challenges demonstrates a level of maturity and accountability that is rare in the fast-moving fintech sector. These reports offer insights into the platform’s incident response capabilities, showing how quickly they can identify a threat, contain the damage, and communicate with their clients. Conversely, a lack of documentation or a history of opaque responses to security events should be viewed as a major warning sign that the provider may not be equipped to handle the complexities of AI-powered heists.
This historical review also helps in assessing how the platform has evolved its standards in response to the broader industry landscape. For instance, evaluating how a provider adapted after high-profile exchange hacks or stablecoin de-pegging events can reveal their commitment to continuous improvement. A serious crypto banking partner will likely have undergone multiple third-party audits and may hold certifications that verify their adherence to international security standards. In an era where autonomous hacking can target any organization, the ability to demonstrate a forensic trail and maintain immutable logs is crucial for both recovery and regulatory compliance. By prioritizing partners with a proven track record of transparency and resilience, business leaders can build a financial foundation that is capable of withstanding the increasingly aggressive tactics of the digital age.
The Path Forward for Digital Asset Security
The landscape of financial security underwent a fundamental shift as the industry moved through the middle of the decade, with the findings from the 2026-2027 period showing that traditional defense models were no longer sufficient against autonomous adversaries. Organizations that proactively transitioned to multi-layered, segregated architectures found themselves significantly more resilient than those that relied on legacy “bank-grade” marketing. The transition involved moving away from centralized points of failure and adopting a mindset where every transaction required verifiable, human-led authorization. This shift was not merely a technical adjustment but a cultural one, where transparency in custody and the rigorous testing of internal permissions became the new standard for corporate treasury management.
Looking toward the 2027-2028 window, the integration of AI-specific risk assessments into standard compliance frameworks will likely become mandatory for any platform handling digital assets. The interplay between regulatory oversight and technological innovation has already begun to favor providers who can demonstrate architectural separation between their transactional and custodial layers. For businesses, the actionable next step involves a continuous cycle of verification and adaptation, ensuring that their chosen financial partners remain at the forefront of defensive technology. By maintaining a disciplined approach to security—focused on the concrete steps of infrastructure examination, authorization separation, and anomaly detection—organizations can continue to harness the benefits of crypto banking while effectively neutralizing the threats posed by the next generation of digital heists.